

What Is XDR, Really? Let’s Face The Confusion
We’ve all experienced that moment of opening up our emails to find a message in our inbox that doesn’t look quite right – perhaps it’s from a stranger, has a suspicious attachment or comes from a colleague (but you know them well enough to know it doesn’t sound like them).
Sometimes, however, these emails aren’t so obvious. In fact, they’re not obvious at all.
Phishing is one of the primary threats facing organisations and the reason they’re so successful is down to just how good threat actors have become at duping victims and exploiting our click-happy society.
Here’s how you can stay vigilant and take actionable steps to counter-act phishing within your organisation.
Seek Actionable Intelligence
You can take better action on what you know; the more knowledge you have of cyber-attacks, phishing campaigns and the key methods used, the better your resiliency against phishing. Whether you are doing your own in-depth research or using a Threat Intelligence team, you can discover what is currently on high alert, how organisations are protecting their employees and predict what to look out for in the near future.

Act Immediately and Decisively
As with all cyber-attacks, time is of the essence. The quicker you react, the more time you have to detect a threat, evaluate it, and take the appropriate action to remediate it. For many security teams, this is a challenge, and in-house SOCs are overburdened with the overwhelming stream of constant security alerts filtering into their system from suspected phish. Organizations need to look to Managed Phishing Detection and Response (MPDR) for a 24×7 threat monitoring service instead, meaning their security teams can focus their attention on incident response, rather than the time-consuming process of evaluating security alerts. With incident response, employees are encouraged to rehearse relevant examples of a cyber-attack to promote confidence and quick reaction should the opportunity arise.
Educate Employees (But this only goes so far)
Although using a MDR service offers the quickest and most accurate response to cyber threats, educating your employees plays a vital part in building awareness and encouraging reporting of suspicious content with a clear method and no-blame culture. In many organizations, a lot of pressure falls upon the security team to check a box for training regulations, but is it being done correctly and effectively? Building phishing simulation scenarios that closely align with what you are most likely to experience will boost your organization’s overall resiliency from phishing as employees learn best practices with confidence. However, educating a workforce and increasing awareness only goes so far, and doesn’t stop the threat from reaching the user. Training and awareness is only effective as part of a wider anti-phishing plan.
Protect Your Accounts
Account takeover is currently the biggest phishing problem. Malicious emails have the capability to bypass even the best software, so it’s important to take your own precautions where possible. Using a proxy server or up-to-date browser can protect users from malicious websites, whilst using multi-factor authentication, or even 2FA, can make you more resistant to phishing via login credentials. You may even want to consider what information is available to attackers on your website and social media. What email addresses are available for them to use to their advantage? Can you update your privacy settings?
This is where services like OSINT can help organisations identify what sensitive information about them is available openly on the internet, and what exposed data can be used by threat actors to create well engineered phishing attacks.
Listen to the Security Noise (or at least some of it)
There’s a lot of chatter online about recent cyber-attacks and method of best practice, and often it can feel like getting lost in a void, but there is some gold. When it comes to security advice, we highly recommend paying attention to:
NCSC – They share four layers you should build your security protections upon. Implementing these multiple layers ensures that if any actions or platforms slip up, there is always a reliable protection right underneath it. You can read about a specific case study example here, or view the infographic below.
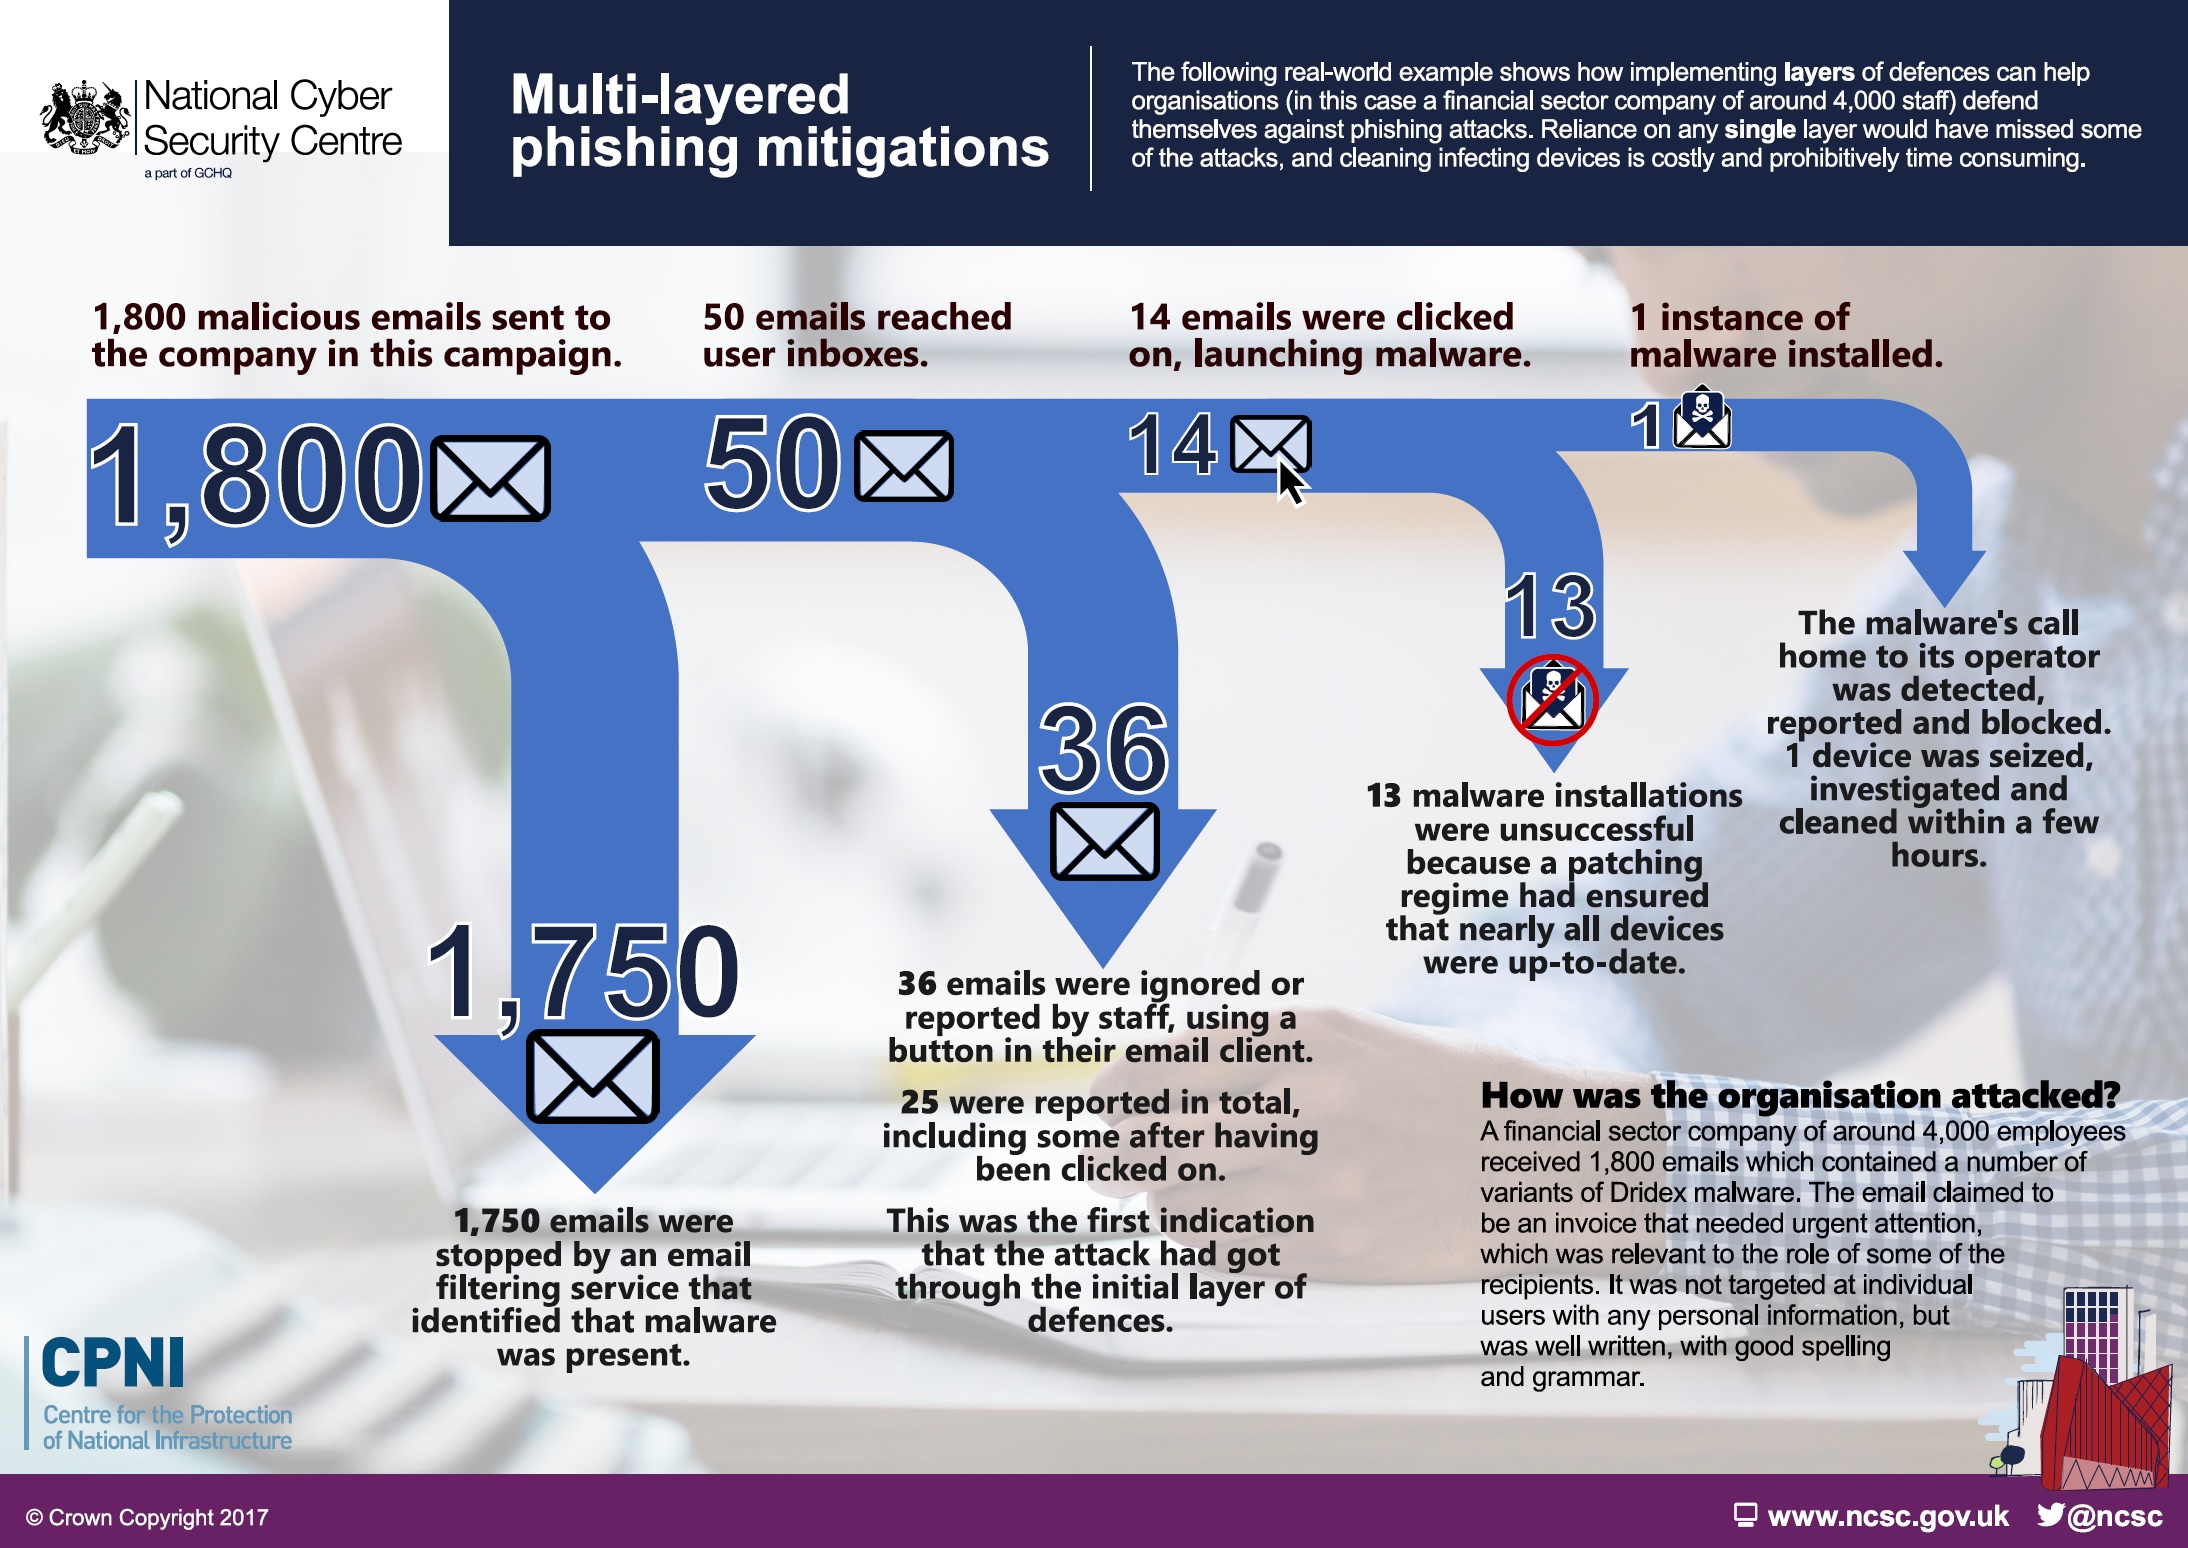
Overall, fighting phishing is most effective when you are executing a combination of anti-phishing solutions, employee education and threat analysis. If you can support your IT security team to identify cyber-attacks quicker and take action, without wasting precious time and resources, that is crucial.
For more information on phishing and how to fight it, read The Ultimate Guide To Phishing – it includes the different methods of phishing, the top phishing spots around the world, and more.
Any questions on how we can help you?
Contact us here.
Threat Intelligence Solutions
Book A Consultation
Any questions? Speak to a Talion team member to hear more about what we do and how we can help you.
Related Blogs

The CISO’s Reckoning: Why Traditional Cybersecurity Models Are Failing
Read More
Watch our demo
- Flexible model; choose your level of interaction
- Full visibility of processes and decisions that are keeping you safe
- Report on any data point from the SOC
- Completely customisable cloud dashboards
- Operate your own SIEM? Collaborate with our analysts
- Approve or reject automated remediation actions
- Get full visibility of your security incidents
