

Going Hybrid: Why Hybrid SOC is the Next Big Thing
4 mins / Alice Davies
Many organisations have poorly integrated security tools, gaps in coverage or spend too much time on routine IT matters rather than responding to significant security alerts.
Hybrid SOC is the way out of this.
After all, why build or flesh out a security team when you have a reliable and efficient SOC right at your fingertips?
In this blog, we cover everything you need to know about hybrid SOC – what it is, the benefits and when you should really consider investing in this solution.
What is Hybrid SOC?
Hybrid SOC is a part-outsourced service executed by a Security Operations Centre, staffed by both in-house security experts and external providers. With 24/7 detection and response, a SOC manages any security alerts on behalf of a company. However, the hybrid approach paired with expert recommendations allows the organisation to have as little or as much control as they want, taking action only where they feel most comfortable. This is unlike a MDR solution, where security is often managed solely by the SOC.
A hybrid SOC model typically offers security tools such as vulnerability management, endpoint protection, security information and event management (SIEM), penetration testing and more. The Talion difference is that our Hybrid solution is underpinned by a threat intelligence team who focus on trend analysis to identify upcoming threats, and combines SIEM and SOAR for maximum efficiency, especially if the number of daily events is high for a limited workforce.
According to the National Cyber Security Centre (NCSC), the key aims of a SOC are:
- to detect and respond to threats, keeping the information held on systems and networks secure
- to increase resilience by learning about the changing threat landscape (both malicious and non-malicious, internal and external)
- to identify and address negligent or criminal activities
- to derive business intelligence about user activities in order to shape and focus on the development of technologies
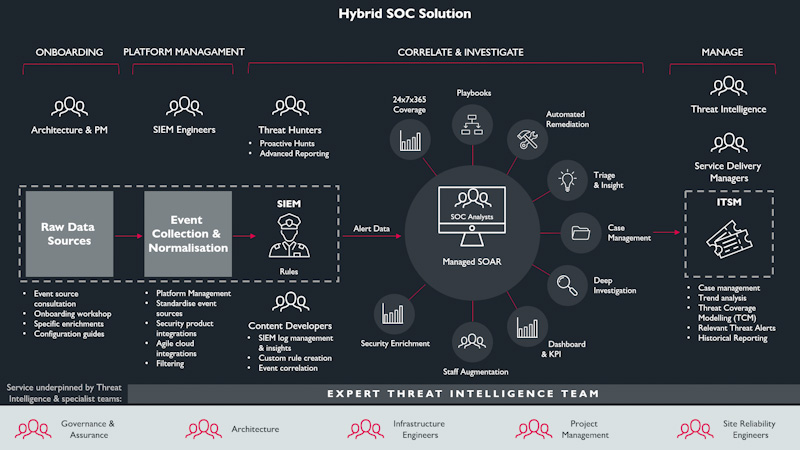
Talion’s Hybrid SOC solution
Benefits of a Hybrid SOC
Building and maintaining a security team requires a huge amount of time, resource, money and investment in in-house talent, with the risk of high staff turnover. By contrast, investing in a SOC-as-a-service not only opens up time for your in-house team to focus on internal tasks, such as incident response, but you know in advance that their group of analysts are experts in the field, with all the tech already set up to do the job.
Here are 5 huge benefits of a hybrid SOC:
✅ An uninterrupted 24×7 service with faster detection and response, without burning out your own security team
✅ Seamlessly integrates with in-house security teams to offer a tailored security approach suitable to your company and industry
✅ Staff augmentation fills the skills gap amongst in-house staff whilst also training them to develop and progress
✅ Saves time and cost of recruitment, especially during the chronic shortage of security experts in the job-hunting space
✅ The ability to “Bring your own Tech” – previous investments are not at a loss; they integrate to increase value
Does Your Company Need a SOC?
Considering whether your company needs a SOC can be a gruelling process – often you need to sit back and evaluate what you already have, in terms of team members, skillset and current output, before you make a decision. Are you doing enough for your security strategy? Would it be worth investing money in a SOC to reduce recruitment time and fees? How about eliminating analyst burnout or increasing the efficiency of managing alerts?
A SOC using staff augmentation to help an group evaluate their existing staff and fill the skills gap with an outsourced expert team – something that is particularly beneficial if your company is struggling to maintain a high enough skillset amongst your hired staff. It also creates a single point of visibility for all of your threats, which can be particularly helpful for organisations with multiple office locations or large quantities of sensitive data that require a smooth, efficient function to protect, without unnecessary complex systems.
If you are looking for a flexible partnership that supports your current security strategies (moulding into your existing investments) but also helps you improve them to increase your overall coverage, then hybrid SOC is the route you’ll want to go.
Talion’s Hybrid SOC
Talion offers a new kind of hybrid SOC. With the integration of Managed Security Orchestration, Automation & Response (SOAR), SIEM content development, bespoke playbook creation, staff augmentation and more, organisations benefit from a SOC that delivers rapid detection and response to security threats, without the headache of deploying new tech and training a team to recognize its full potential.
The most successful hybrid SOCs emphasise flexibility rather than a rigid responsibilities matrix, and this is certainly something that we take pride in at Talion, allowing organisations to have as little or as much input into their security management as they wish. This means one company may choose to invest in Talion’s MDR solution, where we often manage all of the security on their behalf, whilst another may take us up on SOAR and staff augmentation but have us recommend action rather than implement it.
The key to hybrid SOC is protecting organisations’ existing technology investments. No need to give up your data or force yourself away from familiar and perfectly capable software; Talion integrates your existing technology with our best-in-class technology to secure any gaps and give a best of both worlds approach.
Talion’s Hybrid SOC solution consists of the following services: SIEM Platform Management (SPM), SIEM Content Management (SCM), Managed SOAR, Staff Augmentation, Threat Intelligence and Service Management.
See the diagram below for visual insight.

Hybrid SOC doesn’t have to be a shot in the dark.
We hope this has been a helpful overview and gives you a better idea of what a hybrid SOC does and if it is a suitable solution for your company.
For more information on Talion’s Hybrid SOC services, visit our Hybrid SOC & Collaborations Services webpage.
Alternatively, download our Hybrid SOC datasheet.
Any questions?
We’d be happy to discuss them with you.
Reach out to us via email: hello@talion.net
Or give us a call: 0800 048 5775
Threat Intelligence Solutions
Book A Consultation
Any questions? Speak to a Talion team member to hear more about what we do and how we can help you.
Related Blogs

The CISO’s Reckoning: Why Traditional Cybersecurity Models Are Failing
Read More
Watch our demo
- Flexible model; choose your level of interaction
- Full visibility of processes and decisions that are keeping you safe
- Report on any data point from the SOC
- Completely customisable cloud dashboards
- Operate your own SIEM? Collaborate with our analysts
- Approve or reject automated remediation actions
- Get full visibility of your security incidents
