
FIN7 Cyber Tactics – The Return of USB’s, Fake Companies & Teddy Bears
4 mins / Alice Davies
FIN7 are one of the longest running financially motivated threat groups. From “BadUSB” attack methods with teddy bear sidekicks, to the launch of fake security firms, cybercriminals are getting more and more creative with their approaches.
Here’s what we’ve discovered about FIN7’s cyber tactics as they move into the ransomware space, including where they are now and their most recent arrest.
Who are FIN7?
FIN7, also known as Carbanak, are a prolific, Russian-speaking cybercriminal group that are arguably one of the top threats to today’s financial sector. Known for their diverse set of tactics, they have been active since at least 2015, targeting the retail and banking sector through email compromise scams, attacks against of point-of-sale systems and supply chain compromise.
The constant evolution of their toolset means that they are always one step ahead of expectations, or even one step behind in the case of their most recent use of USBs for old school malware – something which many of us believed was a method left in the past.
But where could their custom-made malware and hunt for cash take them next?
The Return of Old School Malware
Remember the days of USB sticks?
With the introduction of the cloud, there is little use of USBs in this current technological era. However, this hasn’t stopped threat group FIN7 from bringing back some nostalgia for their own financial gain.
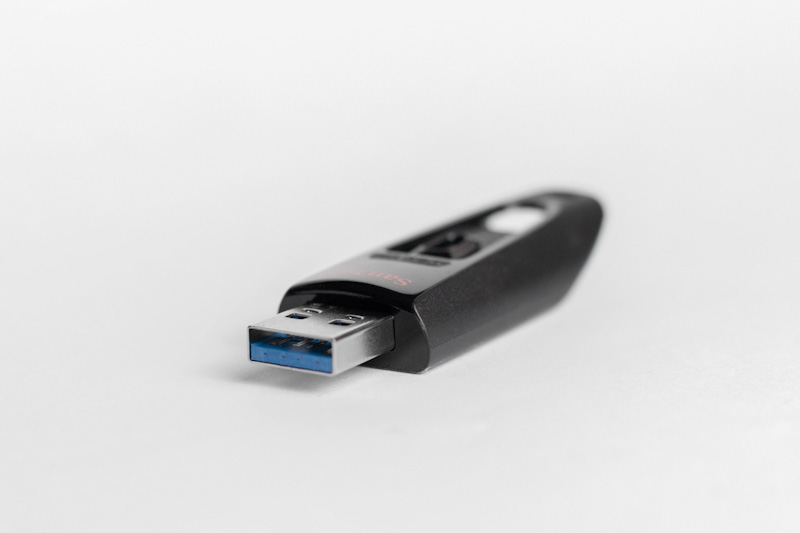
FIN7’s use of the “BadUSB” attack method, targeting insurance, transportation and defense meant hackers leveraged the Arduino platform to create a sketch file called “sketch_jul31a.ino” to install malware on USB devices, connecting to a malicious actor’s file repository and downloading additional software, installing it on the victim’s system.
Back in 2020, FIN7 operators were caught impersonating electronics company Best Buy with packages containing similar malicious USB devices that deploy ransomware. They were sent by the United States Postal Service to hotels, restaurants and retail businesses, containing a “loyalty reward” in the form of a £50 gift card, with a USB drive claiming to contain the lists of products eligible for purchase. Some even included teddy bears to trick the victims into lowering their guard.
However, as expected, these USB drives emulated keystrokes that launched a PowerShell command to retrieve malware from the server controlled by the attacker, before contacting domain or IP addresses in Russia.
FIN7 Launch a Fake Security Firm (Or Two)
FIN7’s impersonation days were not over – in fact, impersonating Best Buy was just a start.
If they could trick victims into believing they worked for an existing company, surely they could trick them into falling for an entirely new (and fake) company if they wanted to. So, they did.
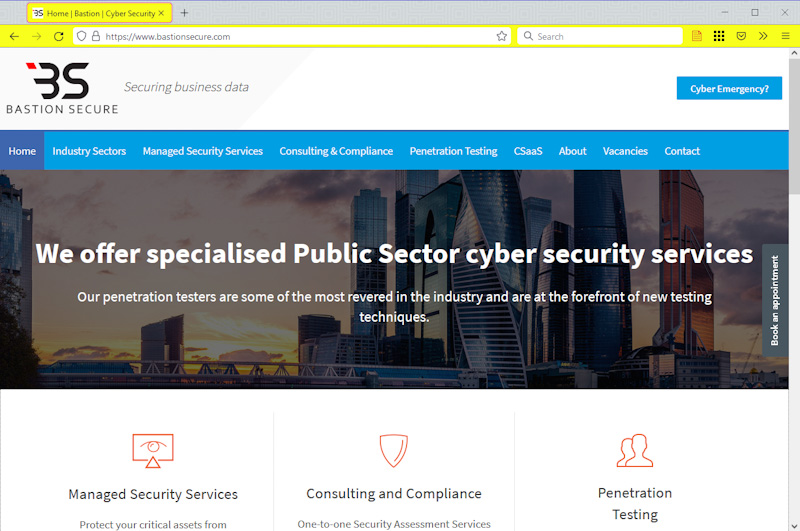
In early 2021, FIN7 set up the fake security company Bastion Secure that claimed to provide penetration testing services for private companies and public sector organisations across the world. Using job portals for Russian-speaking users, they recruited pen testers to map out networks on their behalf, assigning tasks to applicants that mimicked the stages of preparing for a ransomware attack.
Those who applied went through a three-phase interviewing process, involving signing a contract with a non-disclosure agreement and configuring their computer by installing several virtual machines; conducting test assignments using legitimate pen testing tools sent to them, and completing a “real” assignment in person against one of Bastion Secure’s customers.
This wasn’t the first time FIN7 had meddled in this shady process; they had done the same with Combi Security in the mid 2010’s. It seems that hiring a security researcher is a much more cost-effective affair than criminal hackers who would likely demand a percentage of the ransomware payment.
Where are FIN7 now?
There have been notable shifts in FIN7 activity as of late, according to Mandiant, including their use of novel malware, incorporation of new initial access vectors, and shift in commercialization strategies, alongside confirmation that they’ve been working with the likes of REvil and Darkside – the strain behind the colonial pipeline attack.
Most prominently, there has been an evolution of FIN7’s toolset. PowerPlant is being developed into new variants and FIN7 have added new features. Two of the most commonly deployed modules from the C2 server that is fetched by PowerPlant are Easylook (used by FIN7 for at least two years now to capture network and system information like hardware, usernames, registration keys, domain data, etc.) and Boatlaunch (a helper module that patches PowerShell processes on compromised systems).
FIN7 have also developed their Birdwatch downloader which has two variants now – Crowview and Fowlgaze, featuring self-deletion capabilities with embedded payloads. They tell FIN7 what processes run on the system, what the network configuration is and what web browser to use.
A FIN7 Member is Sentenced to 5 Years in Prison
As of April 2022, Denys Iarnak – a Ukrainian national aged 32 – was sentenced to 5 years in prison when found guilty as a penetration tester on behalf of FIN7. Although he was arrested in Thailand back in 2019, he was extradited to the US to stand trial and only now does he face punishment for his involvement in “designing phishing emails embedded with malware, intruding on victims networks and extracting data such as payment card information,” says US attorney Nicholas Brown of the Western District of Washington.
It seems that the arrest and jailtime of his co-conspirators years before did not stop him from continuing work with the criminal enterprise, despite their hefty sentences of 10 years for FIN7 member Fedir Hladyr and seven years for Andrii Kolpakov.
Despite the arrests and convictions of FIN7 members, this cybercriminal group still remains as active as ever. With the continuation of evolved tactics, techniques and execution, they continue to pose ransomware threat to many organisations.
We would like to hear your opinion on FIN7’s tactics – is USB malware still effective, and would you fall for a cyber attack masqueraded as a teddy bear?
Head over to our #RansomAware LinkedIn group to get involved and share any stories of your own.
Threat Intelligence Solutions
Book A Consultation
Any questions? Speak to a Talion team member to hear more about what we do and how we can help you.
Related Blogs

The Impact Of Cyberattacks On IT Security Professionals’ Mental Health
Read More
Ransomware Costs: Beyond The Cash
Read More
Threat Intelligence: Do You Know What Threats You Actually Face?
Read More
Snack Attack!
Read MoreBlurred Lines: Phishing Catches Ransomware Bait
Read More
Phish For Threats: The Emerging Need For MPDR
Read More
5 Tips To Fight Phishing
Read More
Live Debate: Is Cyber Insurance Driving the Ransomware Crisis?
Read More
Your Incident Response Check List
Read MoreWhat Is XDR, Really? Let’s Face The Confusion
Read More
What Impact Does Christmas Have On Cyber Security Teams?
Read More
The Ultimate Phishing Guide (e-Book)
Read More
Strategic Cyber Security Advice for Executives
Read More
Spies at No.10, a $540 Million Crypto Heist & a Botnet Takedown
Read More
Lockbit 2.0 and Conti Overshadow with the Highest Ransomware Activity
Read More
Phishing – What’s The Problem?
Read More
Small Businesses Are Also At Risk of Ransomware Attacks – Here’s Why
Read More
CISO Cyber Dinner Oct 2023 – Recap
Read More
4 Key Takeaways From Cofense’s Email Security Report 2023
Read More
Pros and Cons of AI in Cybersecurity
Read More
LAPSUS$ Cyber Attack
Read More
Is Antivirus Enough To Prevent Ransomware?
Read More
Going Hybrid: Why Hybrid SOC is the Next Big Thing
Read More
FIN7 Cyber Tactics – The Return of USB’s, Fake Companies & Teddy Bears
Read More
Is Cyber Insurance Driving the Ransomware Crisis? Key Roundtable Takeaways
Read More
Cisco Data Breach Shakes The Tech World
Read More
CEO Misconceptions About Paying Ransom: Is It Really A Good Idea?
Read More
12 Days of Cyber Christmas: 2023 Trends & 2024 Outlook
Read MoreThreat Intelligence Update: Dangerous Trends to Monitor in 2024
Read More
Watch our demo
- Flexible model; choose your level of interaction
- Full visibility of processes and decisions that are keeping you safe
- Report on any data point from the SOC
- Completely customisable cloud dashboards
- Operate your own SIEM? Collaborate with our analysts
- Approve or reject automated remediation actions
- Get full visibility of your security incidents
