
What Is XDR, Really? Let’s Face The Confusion
So, what actually is XDR?
Well, depending on who you ask, you’ll probably get a different answer. For an organisation making critical cyber security decision, confusion is the last thing they need.
It also doesn’t help that even top security leaders can’t agree on what it means.
If you ask a technology vendor, it’s an EDR product with Cloud reporting managed by the customer. If you ask an industry analyst, it’s a ‘natural evolution’ of EDR and MDR. If you ask a Managed SOC provider, it’s what they’ve been doing for years, just without the terminology!
We’re here to dispel the misconceptions and simplify what it really means to use an XDR service.
What Does XDR Mean? Here’s OUR Definition!
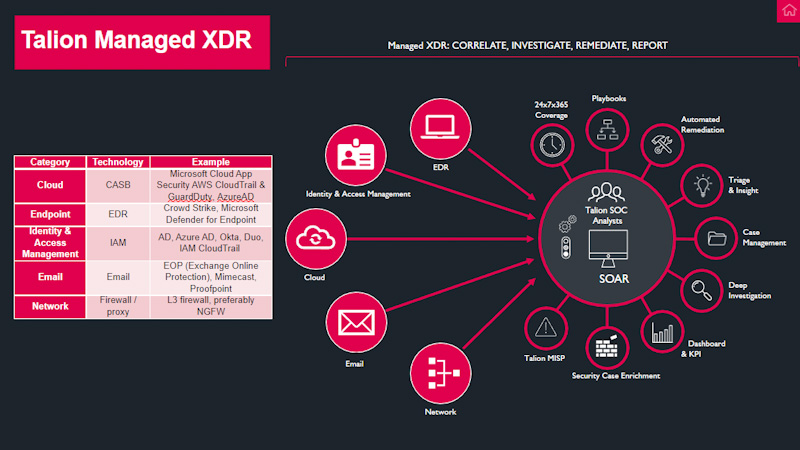
At Talion, we view XDR as a service that goes beyond the End Point with a detection and response service that’s built for your needs, with the flexibility you require. It includes an additional number of core event sources, as well as the endpoint, such as Cloud, Email, IAM and the Network. As a result, it expands upon traditional EDR, with affordability at front of mind. Think MDR-light!
You may ask, how is Talion’s XDR service different to other cybersecurity providers? Especially in a landscape where this term is so often misinterpreted, with little clear explanation…
Talion’s unique standpoint on XDR is that we provide it as a managed service – our team of experts work around the clock to keep organisations safe and secure on all end points AND critical event sources. With as little or as much input as you wish, we offer dynamic visibility into your security threats and actionable recommendations for remediation.
What’s The Difference Between MDR vs XDR?
Managed, Detection & Response (MDR) is a service that acts as a security partnership, managing your security alerts, responding to cyber threats and reducing the risk to your business, all from a centralised Security Operations Centre (SOC). It typically runs on SIEM and SOAR platform capabilities, and Talion’s MDR service is threat-led to ensure we defend against relevant and forthcoming threats.
The difference between an MDR and XDR service is that XDR is seen as an expansion of Endpoint, Detection and Response (EDR), including a limited number of additional core event sources. Whilst MDR is managed solely by the security provider, XDR doesn’t necessarily follow this route, although most companies choose the managed offering to unload the stress and time that comes with acting upon the recommendations given.
As mentioned above, XDR offerings vary per security provider, so be sure to check in with what is and isn’t included when making a decision for your business, in order to find the best provider for you.
As a guide, industry analysts such as Gartner view XDR as including End Point along with Email and IAM. Whilst Talion’s XDR service is similar, we go beyond by including additional core event sources and offering a fully managed service.
Benefits Of XDR
With XDR, you can get the benefit of an MDR offering with an ‘off the shelf’ service built to suit your requirements and your budget.
Talion’s XDR service offers 5 key advantages:
✅ Covers key security event sources
✅ 24/7 fully managed service from industry-leading SOC
✅ Increase your cybersecurity ROI
✅ Detect threats outside of the endpoint
✅ Full transparency, no hidden costs
We hope this article has dispelled some of the confusion surrounding XDR.
Whilst it may remain an ever-changing definition from business to business, Talion’s XDR offering has been developed in depth to provide you with a tailored service that doesn’t require you to sacrifice needs or budget.
Still confused, or got any questions?
Get in touch with us!
Let’s talk about your challenges, concerns and security goals.
Threat Intelligence Solutions
Book A Consultation
Any questions? Speak to a Talion team member to hear more about what we do and how we can help you.
Related Blogs

The Impact Of Cyberattacks On IT Security Professionals’ Mental Health
Read More
Ransomware Costs: Beyond The Cash
Read More
Threat Intelligence: Do You Know What Threats You Actually Face?
Read More
Snack Attack!
Read MoreBlurred Lines: Phishing Catches Ransomware Bait
Read More
Phish For Threats: The Emerging Need For MPDR
Read More
5 Tips To Fight Phishing
Read More
Live Debate: Is Cyber Insurance Driving the Ransomware Crisis?
Read More
Your Incident Response Check List
Read MoreWhat Is XDR, Really? Let’s Face The Confusion
Read More
What Impact Does Christmas Have On Cyber Security Teams?
Read More
The Ultimate Phishing Guide (e-Book)
Read More
Strategic Cyber Security Advice for Executives
Read More
Spies at No.10, a $540 Million Crypto Heist & a Botnet Takedown
Read More
Lockbit 2.0 and Conti Overshadow with the Highest Ransomware Activity
Read More
Phishing – What’s The Problem?
Read More
Small Businesses Are Also At Risk of Ransomware Attacks – Here’s Why
Read More
CISO Cyber Dinner Oct 2023 – Recap
Read More
4 Key Takeaways From Cofense’s Email Security Report 2023
Read More
Pros and Cons of AI in Cybersecurity
Read More
LAPSUS$ Cyber Attack
Read More
Is Antivirus Enough To Prevent Ransomware?
Read More
Going Hybrid: Why Hybrid SOC is the Next Big Thing
Read More
FIN7 Cyber Tactics – The Return of USB’s, Fake Companies & Teddy Bears
Read More
Is Cyber Insurance Driving the Ransomware Crisis? Key Roundtable Takeaways
Read More
Cisco Data Breach Shakes The Tech World
Read More
CEO Misconceptions About Paying Ransom: Is It Really A Good Idea?
Read More
12 Days of Cyber Christmas: 2023 Trends & 2024 Outlook
Read MoreThreat Intelligence Update: Dangerous Trends to Monitor in 2024
Read More
Watch our demo
- Flexible model; choose your level of interaction
- Full visibility of processes and decisions that are keeping you safe
- Report on any data point from the SOC
- Completely customisable cloud dashboards
- Operate your own SIEM? Collaborate with our analysts
- Approve or reject automated remediation actions
- Get full visibility of your security incidents
