
Blurred Lines: Phishing Catches Ransomware Bait
In an online world full of dense content and endless links, it’s not surprising that phishing and ransomware are on the rise.
41% of respondents in a security survey admitted that they “worry about ransomware attacks evolving beyond their team’s knowledge and skillset.”
But what about phishing attacks?
Now that cybercriminals are beginning to use ransomware tactics for their phishing campaigns, the line between these two attacks is blurred. Cyber-attacks are morphing into one another as cyber criminals seek out the most advanced method of taking down their victims.
We’ve researched these latest phishing trends and what you should look out for as a security leader.
The Rise Of Phishing Complexity
Businesses are becoming more in tune with security awareness and training and, alongside the natural advancements in technology, cyber criminals are seeking newer, more efficient tactics to further exploit the vulnerabilities of unknowing victims.
When it comes to phishing, it’s acknowledged that Microsoft is the top target for brand impersonation, with 11,041 unique phishing URLs. Microsoft is a lucrative target not only due to its popularity as a chosen software, but also that it gives hackers the ability to distribute malware, launch ransomware attacks and more once the Microsoft account itself is compromised. The flexibility that makes it so attractive to business users is therefore, ironically, the very reason cybercriminals exploit it.
Recently, there has been talk of custom phishing kits which have been tailored specifically to bypass even the most seemingly protected software, through bypassing multi-factor authentication (MFA) processes. It is due to its unique attributes, such as HTML parsing and lack of domain translation, that security researchers believe that the attackers are using custom adversary-in-the-middle (AiTM) phishing kits to hurdle second authentication and steal email credentials.
Employees of all organisations should be extra wary of opening attachments or clicking links in emails sent from untrusted sources, and always check the URL in the address bar before moving ahead with any form of login process.
Phishing Attacks Borrow Ransomware Techniques
Hackers rip a page off the ransomware book as they begin to tackle phishing attacks in a new manner. The well-known countdown clock, used by ransomware gangs such as LockBit to encourage faster ransom payment, is now being used as a secondary tactic for after victims have clicked the phishing URL to panic them into handing over their passwords.
The tactic uses phishing emails to deliver a message warning the recipient that an attempt to login to their account from a location they have not used before has been blocked and they should click a link to verify their email address. Once clicked, the site displays a countdown clock ticking down from an hour, where the user must enter their username and password to “validate” their account before the countdown hits zero, otherwise it will be deleted.
This sense of urgency is what plays on the victim’s vulnerabilities as they are left in a position of panic, where they are likely to follow the instructions, even though there is no certainty the account will be deleted at all.
If the user targeted by the phishing email enters their login credentials, the site either claims they have used the wrong password or it says the login details are accepted, before redirecting them back to their company home page. In either case, the result is the same – the adversary steals the username and password to use in future attacks.
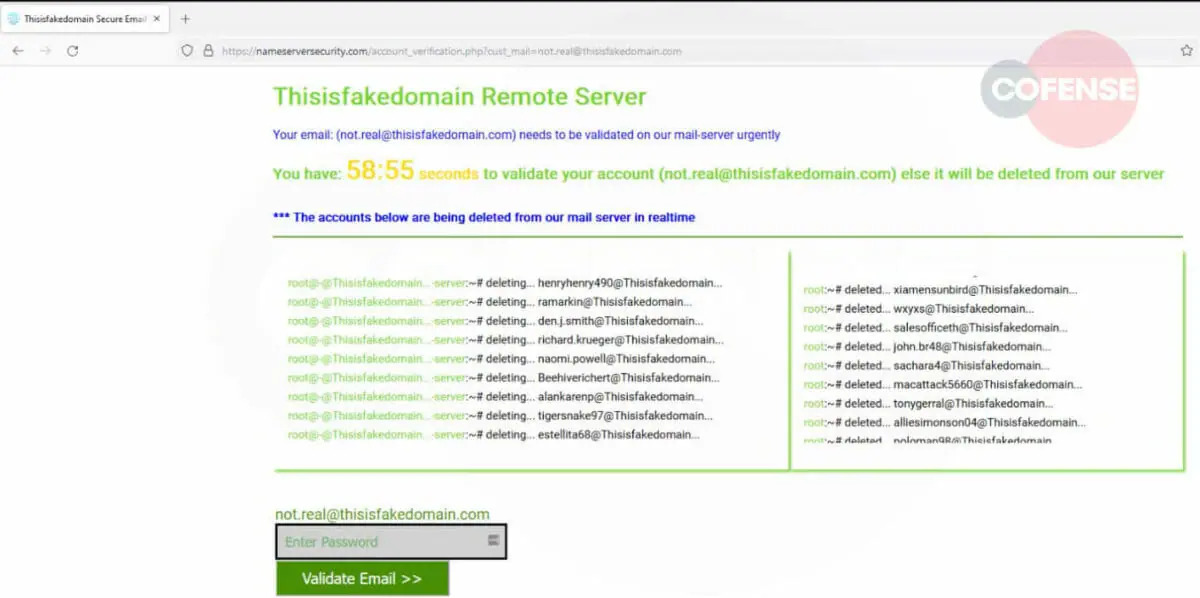
Example of Phishing Attack Countdown Clock
With phishing attacks now using ransomware tactics, the techniques of cyber-attackers are clearly never set in stone – so stay vigilant.
Keep up to date with the latest trends by signing up to our email newsletter and circulate security best practices within your organisation.
Download our Ultimate Guide to Phishing eBook for all the information you need on understanding and tackling phishing – ideal for emailing round to your employees as an awareness guide.
Threat Intelligence Solutions
Book A Consultation
Any questions? Speak to a Talion team member to hear more about what we do and how we can help you.
Related Blogs

The Impact Of Cyberattacks On IT Security Professionals’ Mental Health
Read More
Ransomware Costs: Beyond The Cash
Read More
Threat Intelligence: Do You Know What Threats You Actually Face?
Read More
Snack Attack!
Read MoreBlurred Lines: Phishing Catches Ransomware Bait
Read More
Phish For Threats: The Emerging Need For MPDR
Read More
5 Tips To Fight Phishing
Read More
Live Debate: Is Cyber Insurance Driving the Ransomware Crisis?
Read More
Your Incident Response Check List
Read MoreWhat Is XDR, Really? Let’s Face The Confusion
Read More
What Impact Does Christmas Have On Cyber Security Teams?
Read More
The Ultimate Phishing Guide (e-Book)
Read More
Strategic Cyber Security Advice for Executives
Read More
Spies at No.10, a $540 Million Crypto Heist & a Botnet Takedown
Read More
Lockbit 2.0 and Conti Overshadow with the Highest Ransomware Activity
Read More
Phishing – What’s The Problem?
Read More
Small Businesses Are Also At Risk of Ransomware Attacks – Here’s Why
Read More
CISO Cyber Dinner Oct 2023 – Recap
Read More
4 Key Takeaways From Cofense’s Email Security Report 2023
Read More
Pros and Cons of AI in Cybersecurity
Read More
LAPSUS$ Cyber Attack
Read More
Is Antivirus Enough To Prevent Ransomware?
Read More
Going Hybrid: Why Hybrid SOC is the Next Big Thing
Read More
FIN7 Cyber Tactics – The Return of USB’s, Fake Companies & Teddy Bears
Read More
Is Cyber Insurance Driving the Ransomware Crisis? Key Roundtable Takeaways
Read More
Cisco Data Breach Shakes The Tech World
Read More
CEO Misconceptions About Paying Ransom: Is It Really A Good Idea?
Read More
12 Days of Cyber Christmas: 2023 Trends & 2024 Outlook
Read MoreThreat Intelligence Update: Dangerous Trends to Monitor in 2024
Read More
Watch our demo
- Flexible model; choose your level of interaction
- Full visibility of processes and decisions that are keeping you safe
- Report on any data point from the SOC
- Completely customisable cloud dashboards
- Operate your own SIEM? Collaborate with our analysts
- Approve or reject automated remediation actions
- Get full visibility of your security incidents
